php漏洞补丁已经 发布
8314
- camor2026-10-21

php.net
Security advisory: Critical remote code execution vulnerabilities, update now -...
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately. | PHP is a popular general-purpose scripting language that...
忘了说了,官方说22点,实际补丁提前十几分钟就出来了
主楼 - dalang2026-10-21
我去,7.x的咋修复呀。
- 竹凌2026-10-21
只能交给astra大人了,公司6千块买的小程序后台是PHP做的,我们自己又魔改了不少^-^
- Only_Linux_Can_Do(OL2026-10-21
午时已到,我将化身天才黑客!
- yukinoi2026-10-21
这是世界上最好的大逃杀游戏
- 陈寒彤2026-10-21
- lan2026-10-21
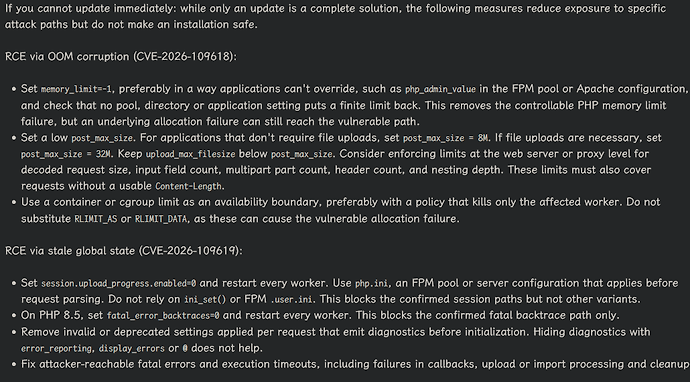
停止维护了,好像有临时抢救方法。
- dalang2026-10-21
事已至此,明天肯定有7.x的修复方法,明天再说吧
- Inex_zero2026-10-21

github.com
GitHub - php/php-src at PHP-7.4-CVE-2026-109618-109619
PHP-7.4-CVE-2026-109618-109619
The PHP Interpreter. Contribute to php/php-src development by creating an account on GitHub.
看源码修呗(
- Xinalin2026-10-21
- everyback2026-10-21
完蛋喽,关session治不好,只有关multipart才有用,一大批不老不新的php站点要完蛋了,官方不把旧版本官方fix发出来基本上就是在拆php老站点的根了
- Cland2026-10-21
一是修改
php.ini配置文件,添加或调整以下配置项,关闭会话上传进度功能并开启严格模式:```
session.upload_progress.enabled = 0
session.use_strict_mode = 1
```修改完成后重启PHP-FPM或对应Web服务,确认配置生效。二是通过WAF、反向代理等边缘程序,收紧
multipart/form-data类型POST请求的检测规则,对无需文件上传的业务端点限制或拦截上传请求,收缩攻击面。 - SomeBottle2026-10-21
在低版本 PHP 补丁出来前可以直接先禁止所有 multipart 请求,比如 nginx 的:```
server {
# 其他现有配置...if ($http_content_type ~ "^\smultipart/") {
return 415;
}# ...
} - Cland2026-10-21
- qwer32342026-10-21
旧项目有不少都是7.4版本,这下完犊子了 ^-^